Independent Canadian cybersecurity · Ottawa, OntarioClarity, not complexity.
01 / Security advisory

Know where you stand. Plan what comes next.

Practical security posture reviews and ISO/IEC 27001:2022 readiness guidance for organizations that want clearer priorities.

Discuss an assessment
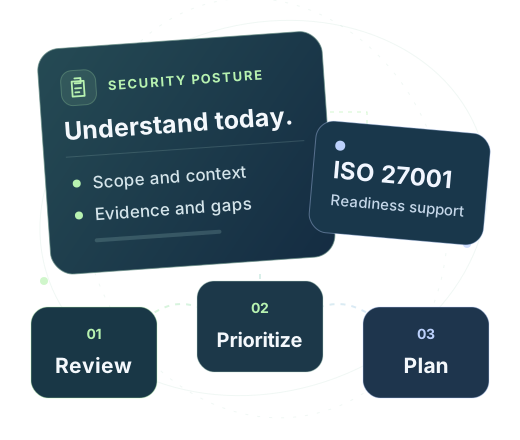
Illustrative advisory approach: review current posture and evidence, prioritize gaps, and plan improvements, with ISO 27001 readiness support.
Clear scope. Evidence. Practical next steps.
Focused offering

An assessment built
around decisions.

Our core engagement helps teams understand existing practices, identify gaps and organize a sensible improvement plan.

Starting point / Core offering

ISO 27001
readiness review

Map current practices and available evidence against applicable ISO/IEC 27001:2022 ISMS requirements and agreed Annex A controls.

  • Internal and external organizational context
  • ISMS scope, risk and governance gaps
  • Actionable evidence and improvement priorities
  • ISMS implementation support within an agreed scope
Discuss readiness →
Complementary / For SMEs

Security posture
& risk assessment

For organizations not yet seeking certification: build a baseline view of risks and practical safeguards using an agreed framework and business context.

  • Assets, dependencies, and likely exposures
  • Baseline control and process review
  • Risk-based priorities suited to your capacity
Discuss your needs →

Important: These are advisory and readiness services. They are not accredited certification audits, and no particular certification result is promised.

A transparent process

From scope to
practical next steps.

The precise effort depends on your size, systems, existing documents, and target outcomes.

STEP / 01

Scope

Define objectives, organizational boundaries, relevant parties, and the evidence to review.

STEP / 02

Assess

Review interviews, policies, operations, and available information against agreed criteria.

STEP / 03

Prioritize

Evaluate deficiencies based on risk, impact, dependency, and implementation effort.

STEP / 04

Plan

Deliver findings and a roadmap the people responsible can act on.

Agreed deliverables

What an engagement
is designed to leave behind.

Current-state overview

A defensible summary of the organization's posture, assessment scope, and limitations.

Gap and evidence register

Relevant missing controls, documents, processes, and supporting observations.

Prioritized risk actions

Recommendations grouped by impact and feasibility, with clear rationale.

Leadership discussion

A readable summary and working session to decide ownership and next steps.

◎

Readiness consulting is not certification.

ISO/IEC 27001 certification is assessed and issued by an independent certification body. ByteDefender may provide advisory and preparation support within an agreed scope, but cannot issue a certificate or guarantee an audit outcome. Training and awareness can support the ISMS; they are not a substitute for its other requirements.

Before you begin

Frequently asked
questions.

Do we need to pursue certification immediately?

No. A security posture or gap review can identify foundational improvements before a certification decision. Your business needs should guide the scope.

Is the scope fixed?

We would agree on a bounded scope and deliverables in writing before any engagement begins. Timing and price depend on that scope and available information.

What about staff awareness and training?

Relevant information security awareness and training are part of operating a sound ISMS. We can discuss them as a separate Academy workstream, aligned to your organization’s actual roles and risks.

What if our team already has an ISO framework?

The review can focus on documented evidence, implementation effectiveness, identified gaps and ongoing program maturity instead of starting again from zero.

Security advisory

Get clarity before committing to complexity.

Start with a short conversation about your organization, goals, and assessment scope.

Discuss an assessment